
GitHub Adds Bulk Start for AI Scan in Repositories (Public Preview)
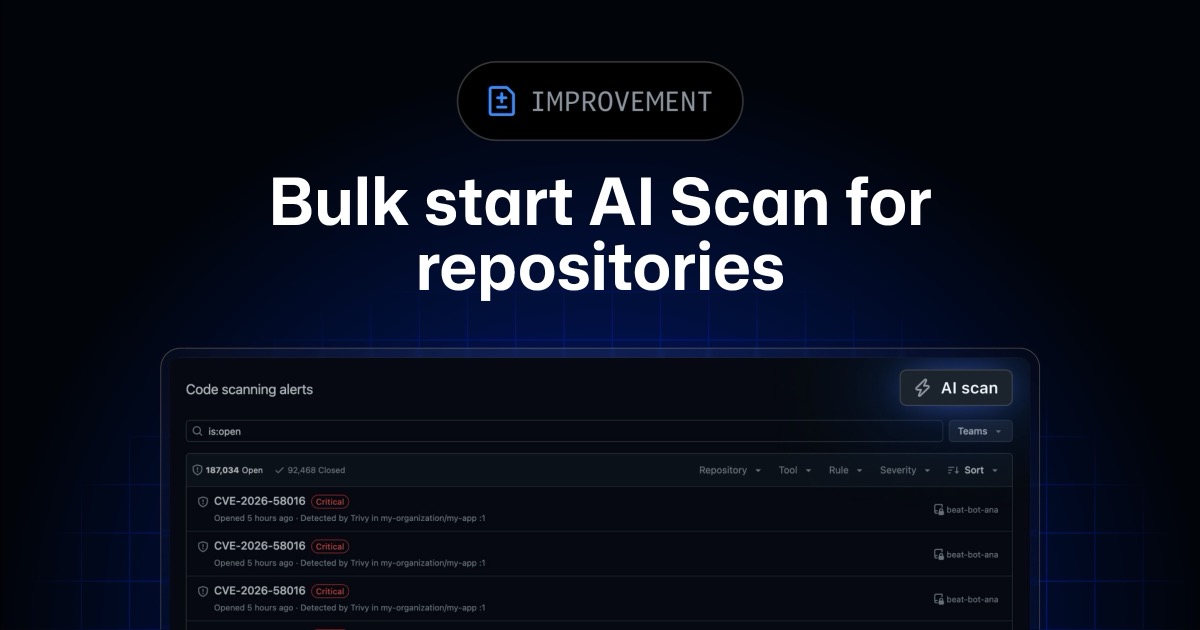
GitHub now allows users to initiate AI security scans across up to 20 repositories at once, making it easier to find vulnerabilities in both CodeQL and non-CodeQL languages.
What changed?
GitHub has introduced the ability to start AI Scans on up to 20 repositories simultaneously. Previously, AI Scans could only be initiated on individual repositories. Bulk scanning can be triggered either from the organization-level setting or via the code scanning organization alerts page. The feature is now in public preview for users on github.com and GitHub Enterprise Cloud with data residency.
Why does it matter to an everyday developer?
This update enables faster, broader security coverage, especially for organizations managing multiple repositories. AI Scan covers languages that CodeQL does not support and finds additional issues in existing CodeQL-supported languages, centralizing results in the code scanning backlog alongside regular CodeQL alerts. Developers can more efficiently scan large sets of repositories for vulnerabilities without repetitive manual steps.
What can the developer do now?
Developers and organization administrators can now select up to 20 repositories and initiate AI security scans in bulk. To use the feature, navigate to the code scanning organization alerts page or enable it through the organization-level setting. For individual repositories, scans can still be triggered directly from their respective alerts pages. No changes to licensing are required, and AI Scans are available for all repositories on github.com and GitHub Enterprise Cloud with data residency.
