
GitHub Adds AI Scan Metrics to Security Overview for Pull Requests
GitHub introduces new organization-wide and enterprise-wide metrics for AI Scan findings on pull requests, with expanded visibility in the security overview. These insights help security teams assess the adoption and effectiveness of AI-powered code scanning workflows.
What changed?
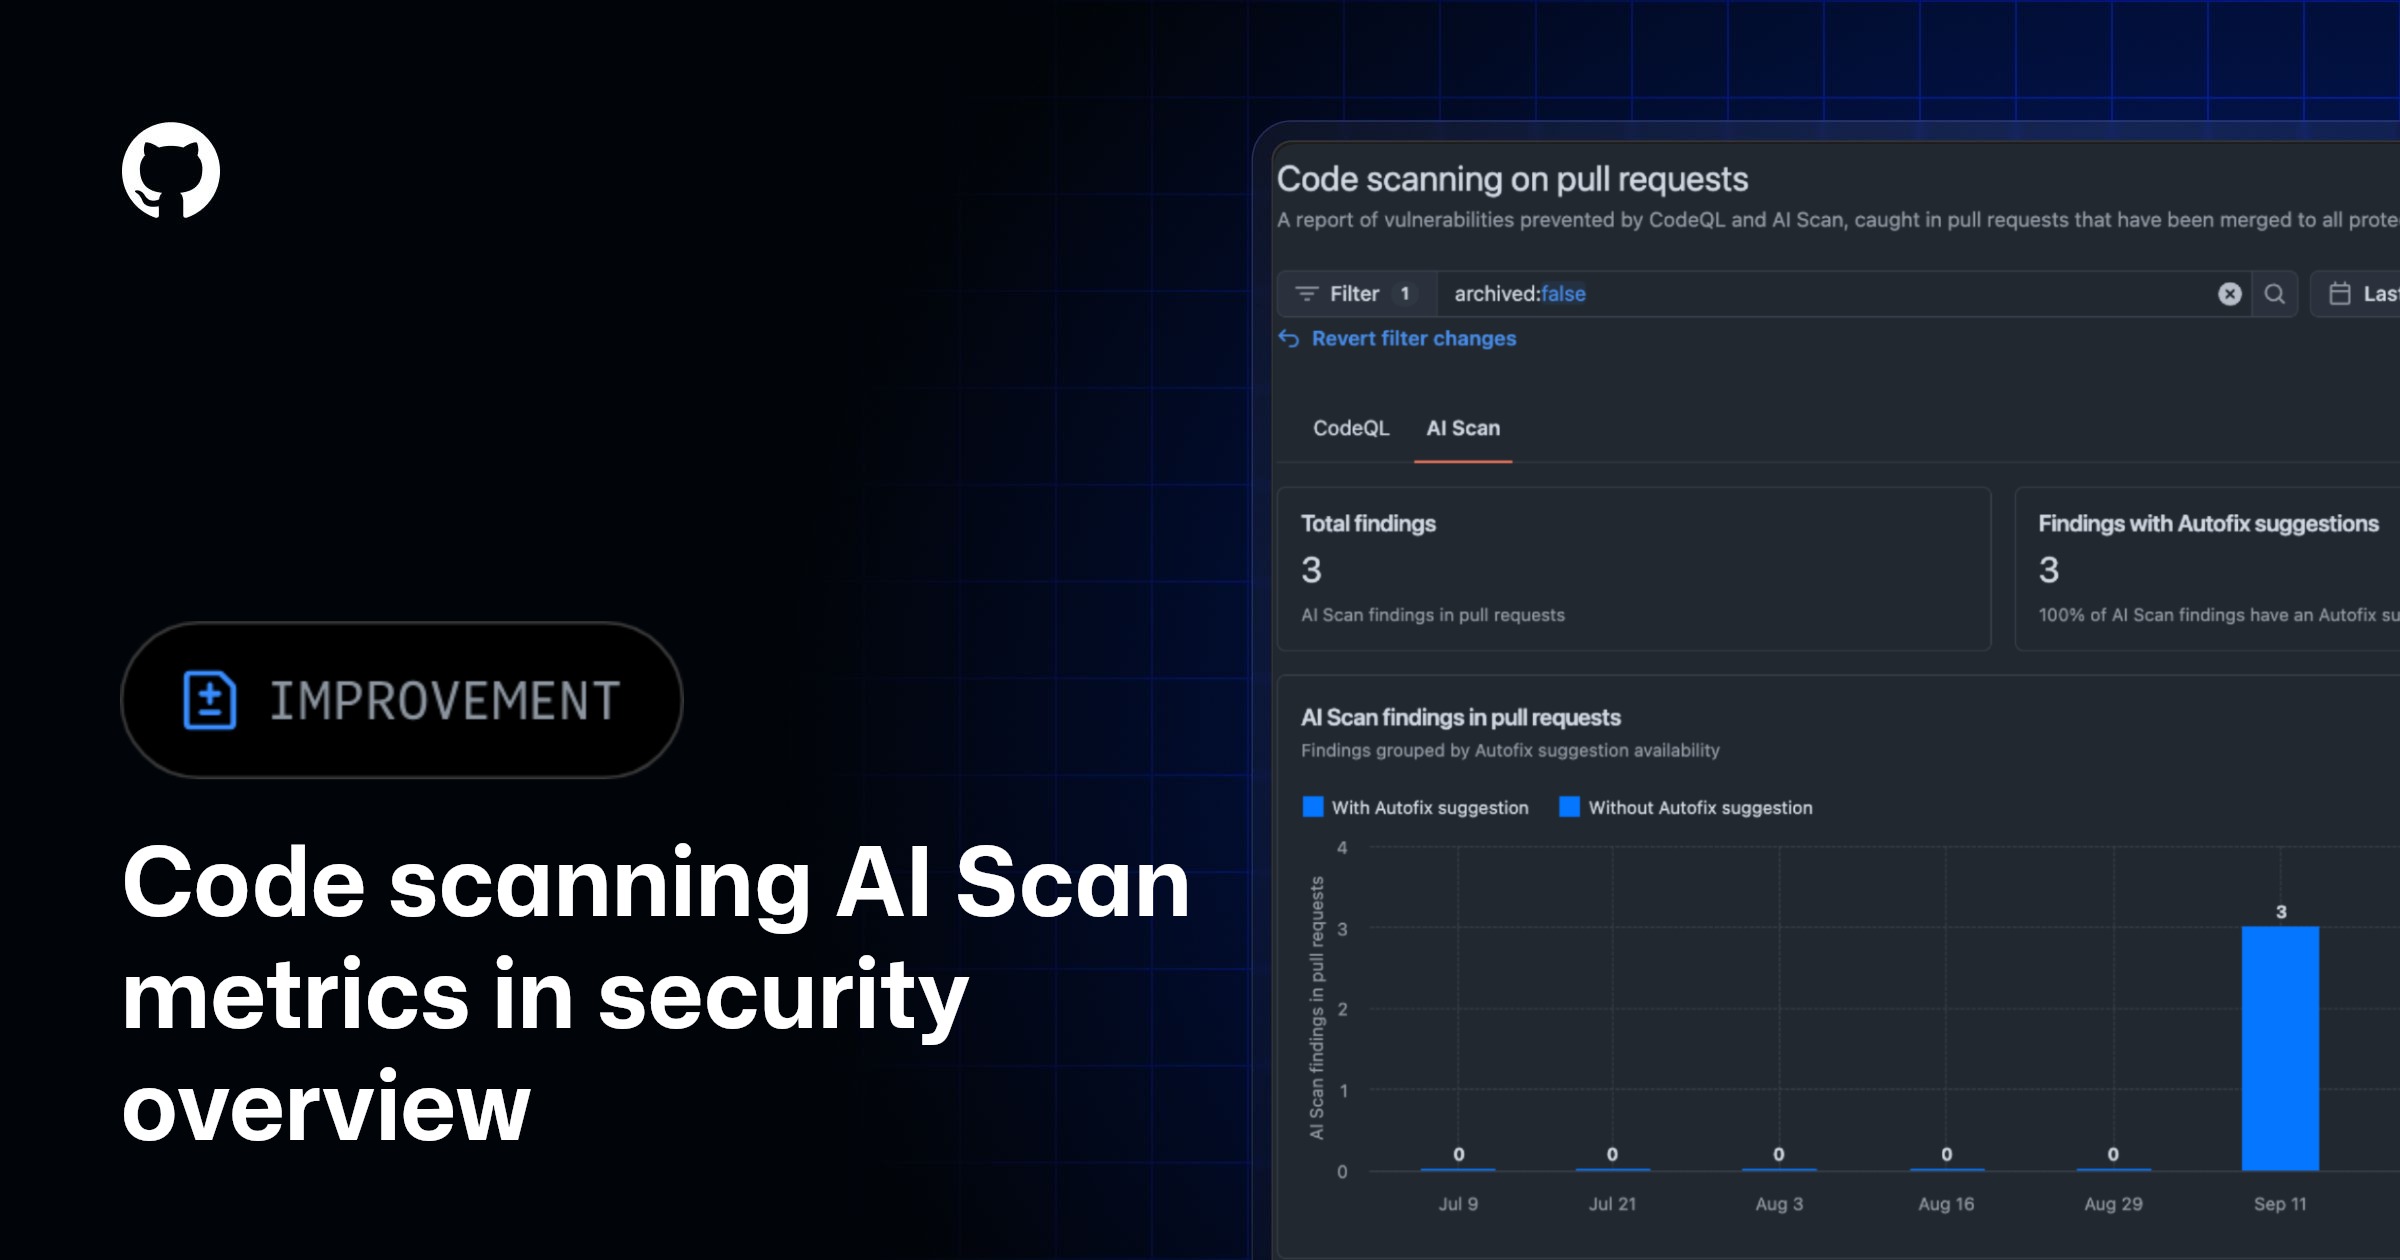
GitHub has added new AI Scan metrics to the security overview for pull requests. Organization and enterprise administrators on github.com and GitHub Enterprise Cloud can now monitor the impact of AI Scan by viewing statistics such as the number of findings generated and resolved, remediation rates, affected repositories, usage trends, and frequency of autofix suggestions being applied. The former 'CodeQL pull requests' page has been renamed to 'Code scanning on pull requests' and now includes separate tabs for CodeQL and AI Scan results.
Why does it matter to an everyday developer?
These visibility improvements help security and engineering teams evaluate the effectiveness of AI-driven code scanning across their repositories. Developers may receive better-informed feedback and autofix suggestions for vulnerabilities. Teams can track the adoption and resolution rates of AI Scan findings at scale without manually reviewing each pull request. This supports targeted developer training, workflow improvements, and investment in automation.
What can the developer do now?
If your organization uses GitHub Code Security or GitHub Advanced Security in the cloud, you can view the new AI Scan metrics in the security overview section. Use these insights to understand where codebase vulnerabilities are most commonly found and how quickly issues are being addressed. Individual developers may notice changes in how autofix suggestions are surfaced or in organizational reporting, but no action is required unless your workflows or adoption of AI Scan is being evaluated. GitHub Enterprise Server users are not affected by this release.