Databricks Apps GA with On-Behalf-Of-User Authorization
Databricks Apps now allows developers to build and deploy permission-aware applications using on-behalf-of-user authorization, making it easier to respect user-level data permissions within the Databricks platform.
What changed?
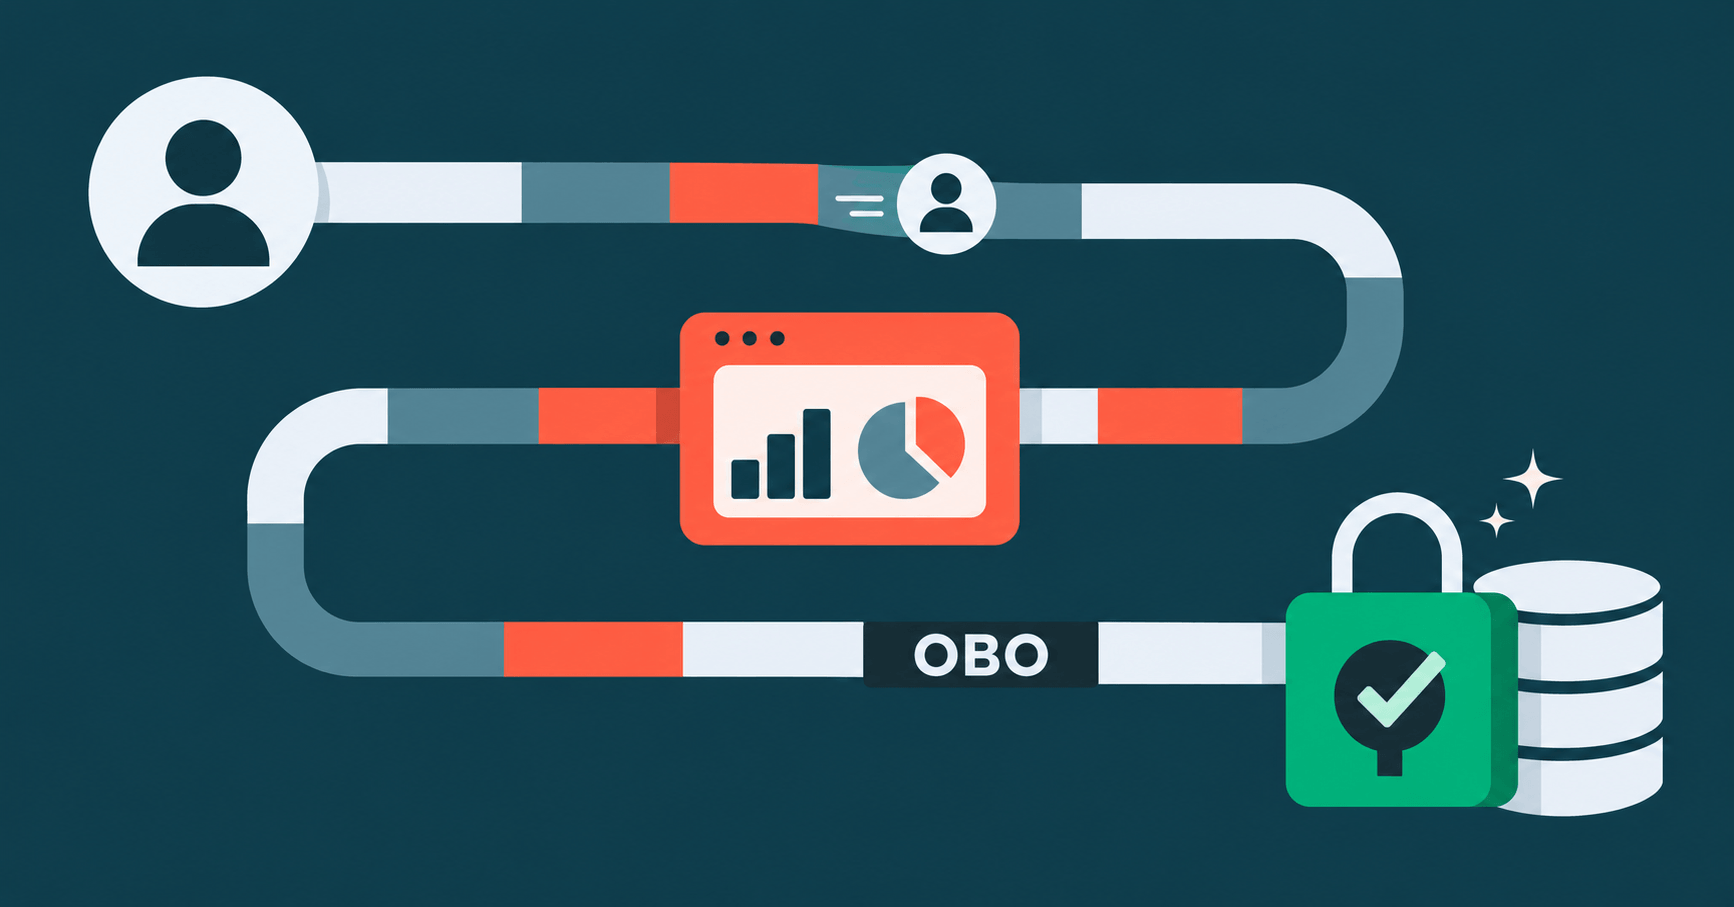
Databricks Apps with on-behalf-of-user authorization is now generally available. Developers can now build and deploy data and AI applications directly on the Databricks platform that are permission-aware and operate according to the end user's data access rights.
Why does it matter to an everyday developer?
This update makes it much simpler to develop applications that respect and enforce Databricks workspace permissions at a granular user level. Applications can securely access only the data users are authorized to view or manipulate, which is essential in environments with sensitive or regulated data. This reduces the complexity of managing security and compliance in custom application development within Databricks.
What can the developer do now?
Developers can leverage the on-behalf-of-user authorization model to build and deploy applications directly on Databricks, ensuring each user's permissions are automatically enforced. This enables custom applications and workflows that align tightly with organizational security policies. Developers should review Databricks documentation on application development and use this model for apps needing user-context data access.